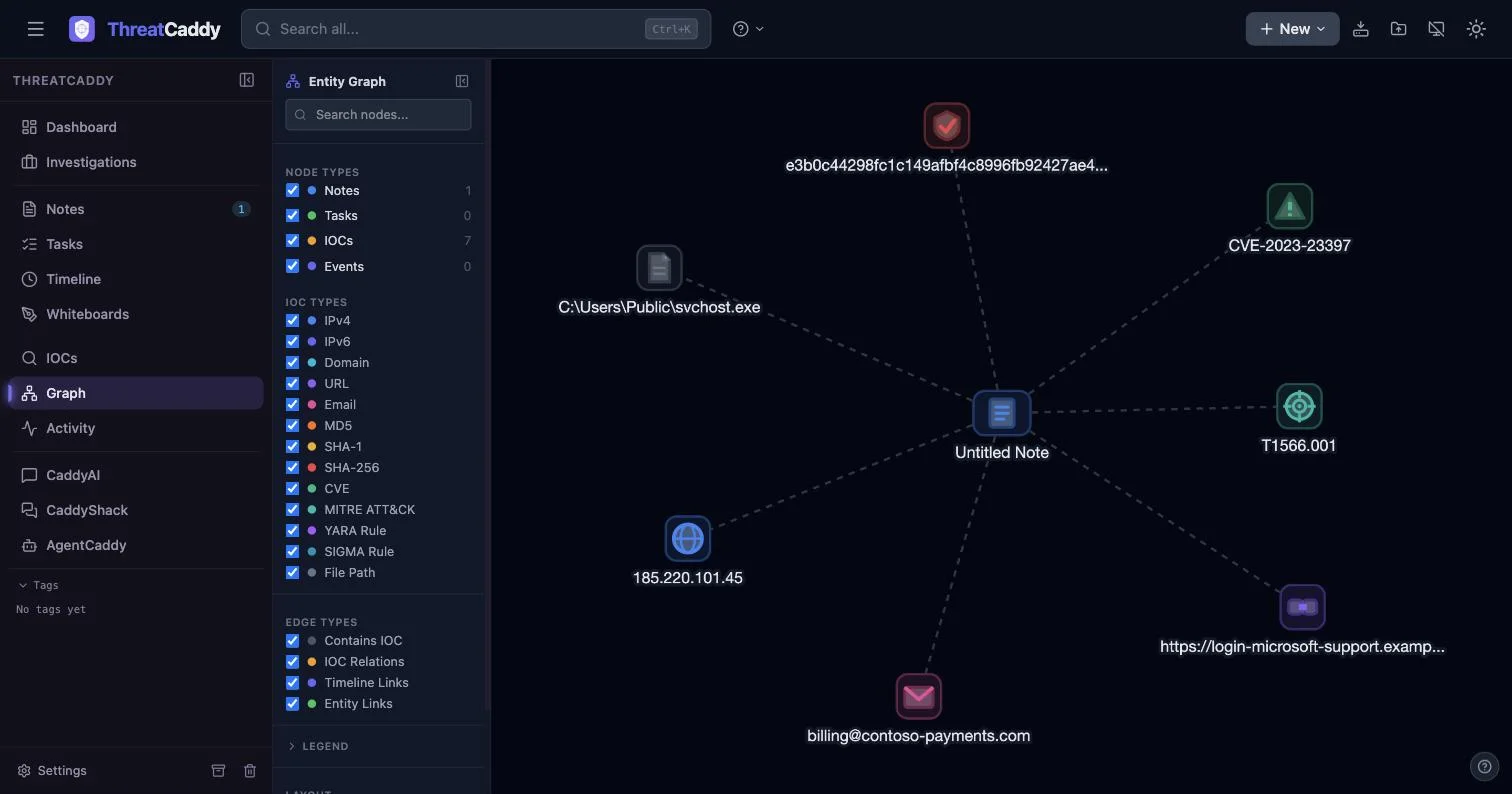
The Browser Is the Case File: A Local-First Investigation Workspace with ThreatCaddy
Most incident response tooling forces a bad choice on you early in a case. Either you’re in a spreadsheet or a plain notebook with no structure, or you’re setting up a cloud platform with procurement friction, a rigid schema, and a data residency conversation before you’ve even confirmed the phishing email is real. Neither one matches the actual shape of early-stage IR work: messy notes, indicators that need pulling out and tracking, and relationships between them that you don’t know yet. ...