Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →

Welcome. My work explores a single, critical question: How do we master the tools of a complex digital world?

Whether it’s deploying a Kubernetes cluster, automating a workflow, or, most recently, partnering with artificial intelligence, my goal is the same: to move beyond simply using technology and toward directing it with strategy, wisdom, and insight.

I’ve codified my framework for this new era of work in my book, The Centaur’s Edge: A Practical Guide to Thriving in the Age of AI. It provides the mindset and practical exercises needed to turn AI from a mysterious force into a powerful partner.

This blog is my workshop for that ongoing journey. I’m glad you’ve joined me.
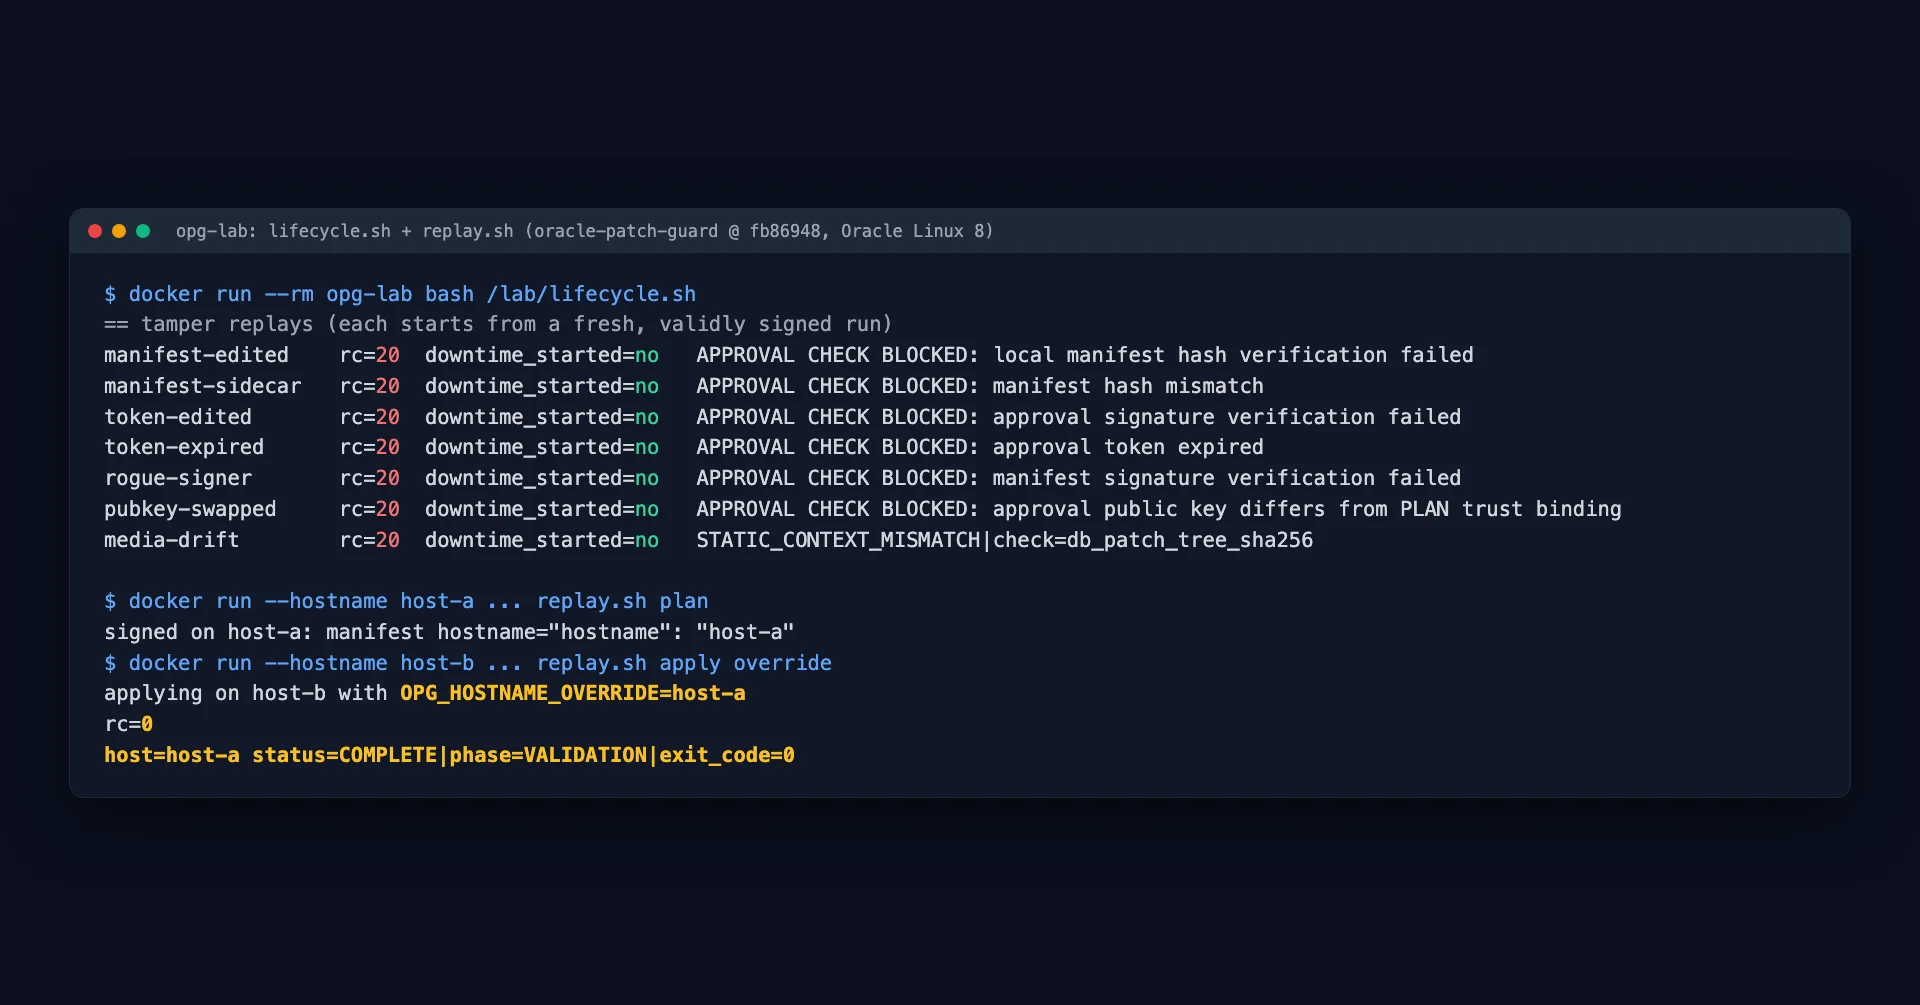
A terminal from the lab. Seven tamper replays against Oracle Patch Guard each end in status BLOCKED with exit code 20 and downtime_started no, each naming a different check: local manifest hash, manifest hash mismatch, approval signature, token expired, manifest signature, public key differs from PLAN trust binding, and a patch tree hash mismatch. Below, a second container with hostname host-b sets OPG_HOSTNAME_OVERRIDE=host-a and applies host-a's signed approval, ending with status COMPLETE and exit code 0.

Signing the Maintenance Window: Testing Oracle Patch Guard's Approval Chain

Patching a production database is the most privileged routine change most teams make. Someone stops the database, rewrites the software it runs on, restarts it, and runs SQL against the data dictionary, usually in a window at 2 AM. The decision to do it lives somewhere else entirely: a change ticket, a meeting, a “yes, go ahead” in chat. Nothing technical connects the thing that was approved to the thing that actually runs. If the patch file changed since Tuesday, the target is a different server, or the backup the change board was promised failed last night, the 2 AM operator usually finds out afterward, if at all. ...

November 17, 2026 · 35 min · Scott Algatt
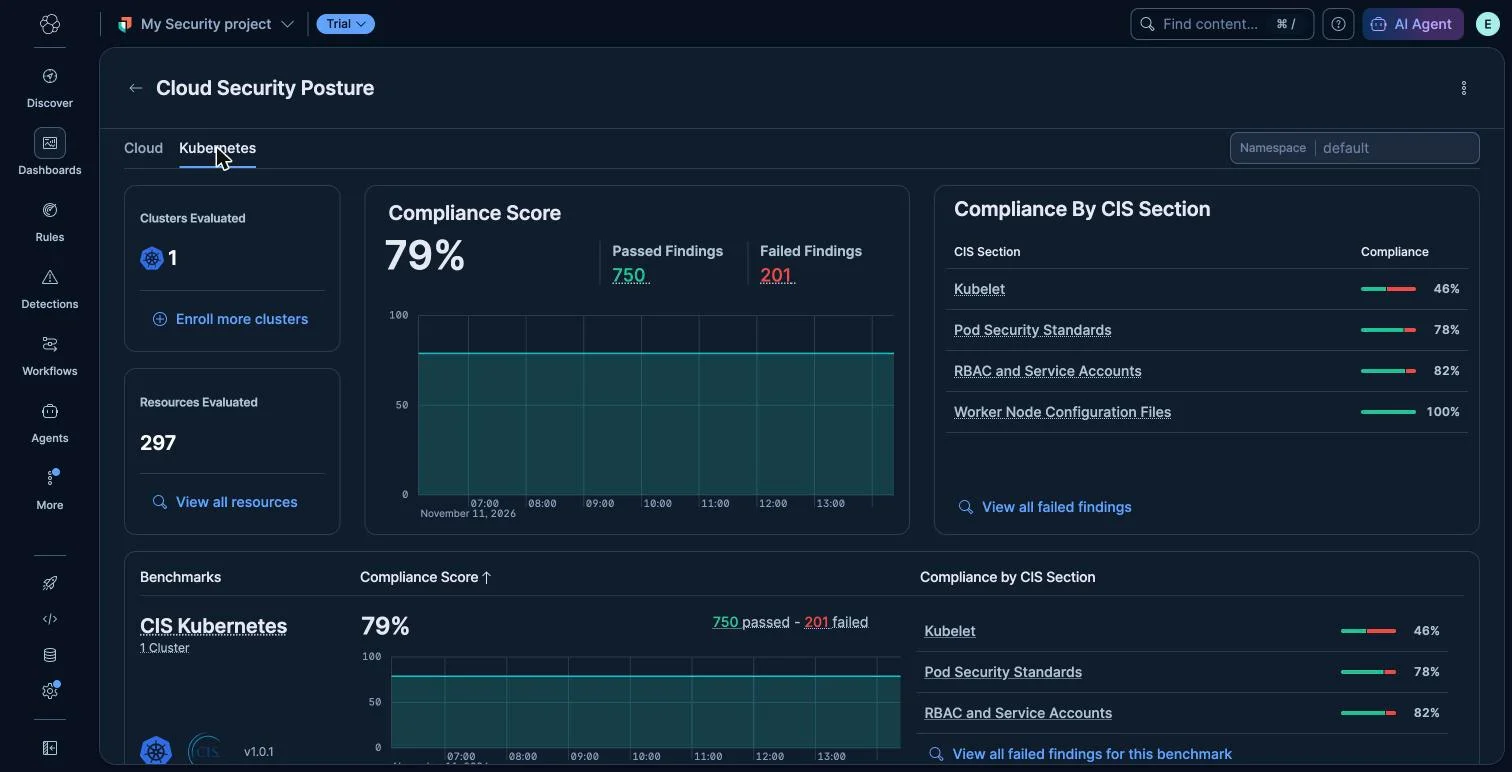
Kibana's Cloud Security Posture dashboard, Kubernetes tab, showing my DigitalOcean cluster at 79% compliance with 750 passed and 201 failed findings, broken down by CIS section with Kubelet at 46%, and a benchmark card reading CIS Kubernetes v1.0.1.

Grading My Own Cloud: cloudbeat, Keyless CSPM, and the CIS Edition Behind the Score

Nobody reviews their cloud configuration by hand. There is too much of it, it changes under you, and the dangerous mistakes (a storage bucket opened to the world, an admin account with no second factor, a node agent that will answer anonymous requests) don’t announce themselves. Vulnerability scanners don’t help much here either; they look at the software running on a host, not at whether the host’s own control plane is set up the way it should be. That gap is what posture management tools exist to fill: pull the configuration out of the cloud APIs, compare it against a published checklist, and tell you what fails. ...

November 13, 2026 · 28 min · Scott Algatt
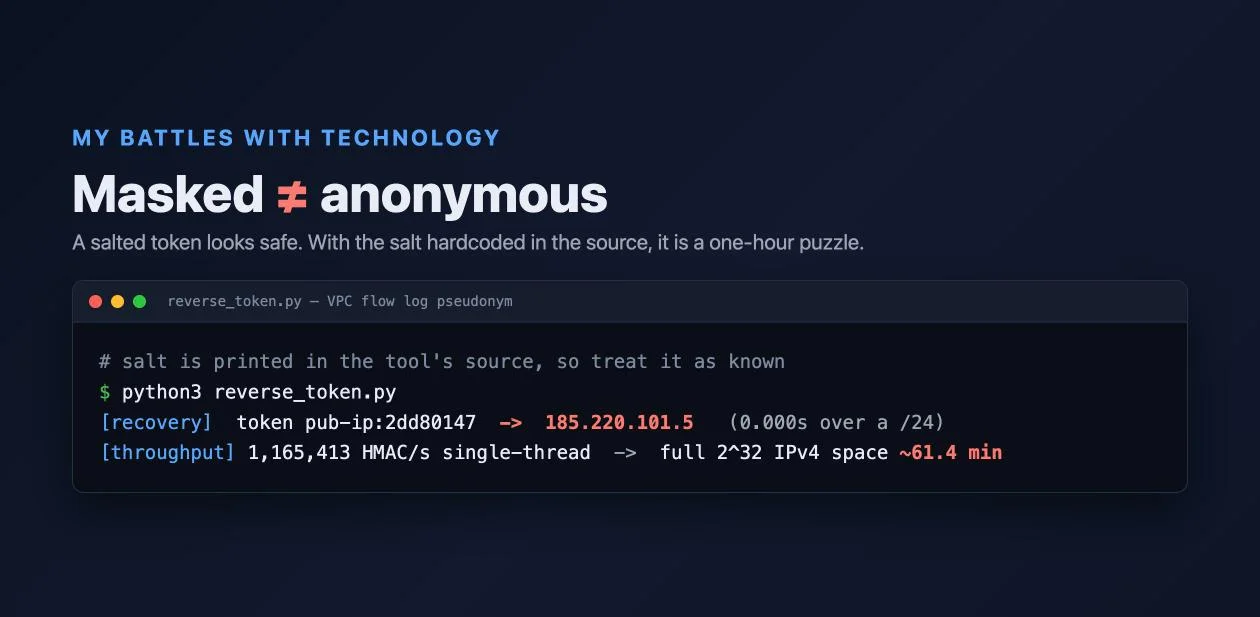
A terminal showing a masked VPC flow log token pub-ip:2dd80147 being reversed back to the real IP 185.220.101.5 in a fraction of a second over a /24, with a throughput line extrapolating the full IPv4 space to about 61 minutes on one core.

Enrich First, Mask Second: An LLM-Safe VPC Flow Log Boundary

Say you run a security operations center and you want an AI copilot to help triage network traffic. The raw material is sitting right there: AWS VPC Flow Logs, a line per network connection, millions of them a day. Pasting them into a hosted large language model (an LLM, the kind of model behind Claude or ChatGPT) feels like it should just work. The problem is what a flow log line actually contains: your internal IP layout, your AWS account number, the identifiers of your network cards. Hand that to a third-party service and you have shipped a map of your private network to someone else’s computer, where it may be logged, cached, or used for training. ...

November 10, 2026 · 19 min · Scott Algatt
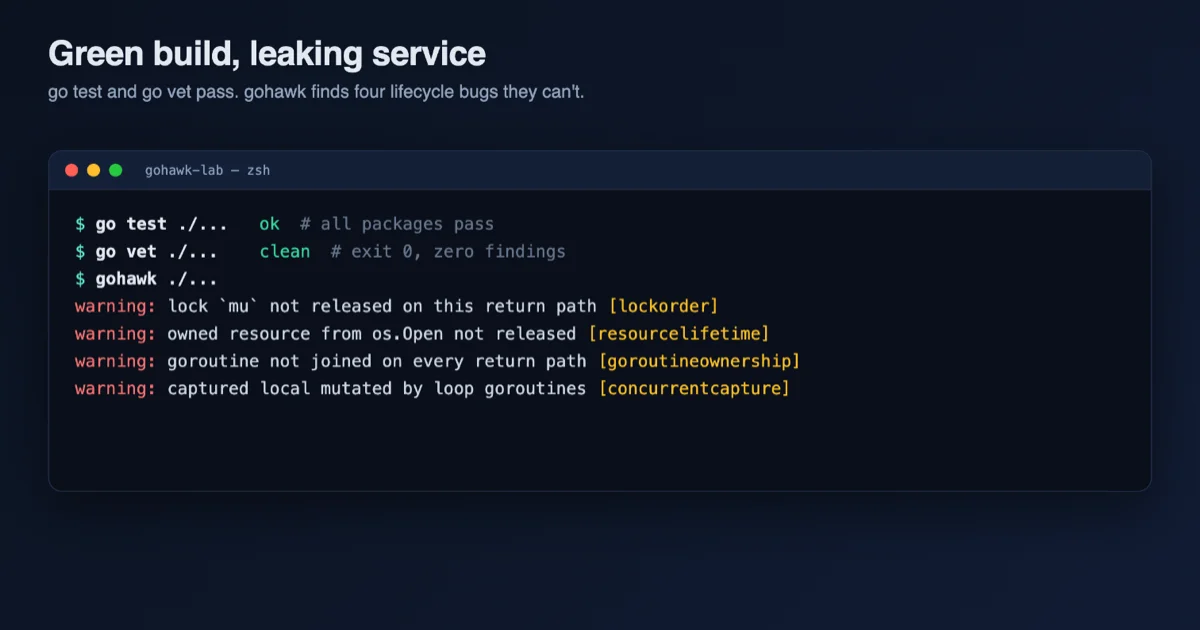
A terminal showing go test and go vet passing while gohawk reports four warnings: lockorder, resourcelifetime, goroutineownership, and concurrentcapture

Green Build, Leaking Service: Static Analysis for Go Concurrency and Resource Bugs with gohawk

A Go service can pass every test, clear go vet without a word, and still be quietly broken. The kind of bug I mean does not throw an exception or fail an assertion. It leaks. A file handle that never gets closed, a goroutine that nobody waits for, a lock that an early return skips over. Each one is invisible on a laptop with a single request in flight, and each one turns into a 3 a.m. incident once real traffic arrives: file descriptors exhausted, memory climbing with abandoned goroutines, a handler wedged on a lock that was never released. ...

November 6, 2026 · 21 min · Scott Algatt
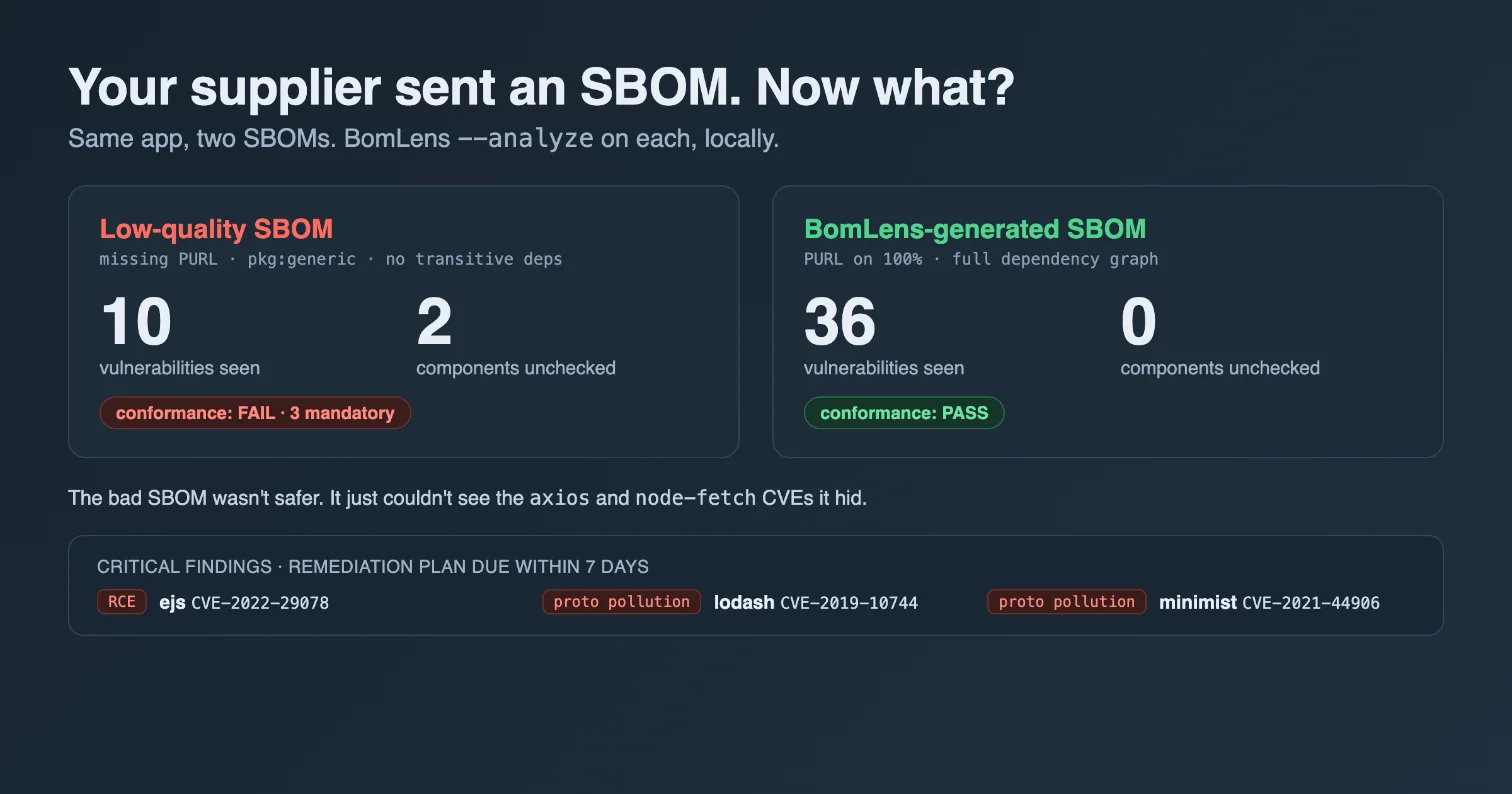
Two cards compared side by side. A low-quality SBOM shows 10 vulnerabilities seen, 2 components unchecked, and conformance FAIL with 3 mandatory failures. A BomLens-generated SBOM shows 36 vulnerabilities seen, 0 unchecked, conformance PASS. Below, three critical findings with a 7-day deadline: ejs CVE-2022-29078, lodash CVE-2019-10744, minimist CVE-2021-44906.

Your Supplier Sent an SBOM. Now What?: Turning CycloneDX Into Risk Decisions with BomLens

Here is a situation that has quietly become everyone’s problem. A vendor ships you a piece of software, and along with it a file called bom.json. It is a Software Bill of Materials, or SBOM: a machine-readable list of every open-source component inside that software, the same way a packaged food lists its ingredients. Regulators now ask for these, procurement teams now demand them, and your own security team now receives them. So the file lands in your inbox. Now what? ...

November 3, 2026 · 20 min · Scott Algatt