Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
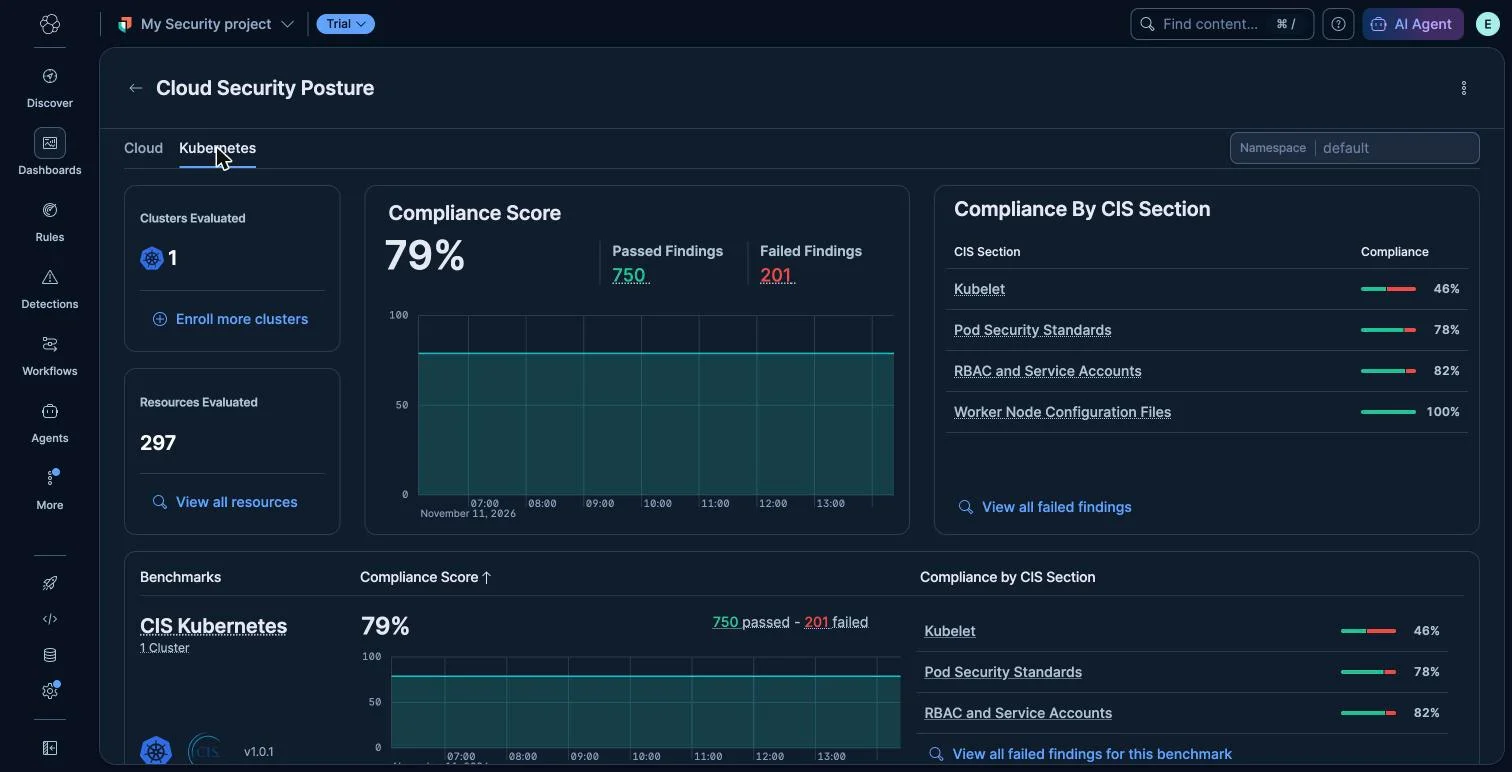
Kibana's Cloud Security Posture dashboard, Kubernetes tab, showing my DigitalOcean cluster at 79% compliance with 750 passed and 201 failed findings, broken down by CIS section with Kubelet at 46%, and a benchmark card reading CIS Kubernetes v1.0.1.

Grading My Own Cloud: cloudbeat, Keyless CSPM, and the CIS Edition Behind the Score

Nobody reviews their cloud configuration by hand. There is too much of it, it changes under you, and the dangerous mistakes (a storage bucket opened to the world, an admin account with no second factor, a node agent that will answer anonymous requests) don’t announce themselves. Vulnerability scanners don’t help much here either; they look at the software running on a host, not at whether the host’s own control plane is set up the way it should be. That gap is what posture management tools exist to fill: pull the configuration out of the cloud APIs, compare it against a published checklist, and tell you what fails. ...
November 13, 2026 · 28 min · Scott Algatt
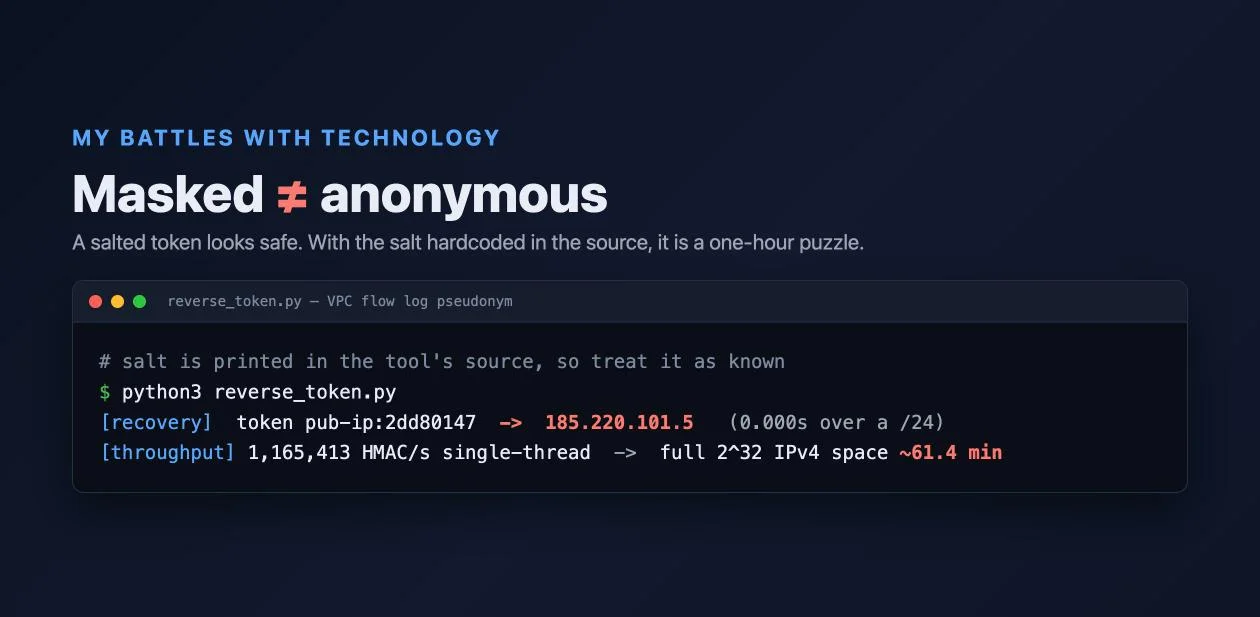
A terminal showing a masked VPC flow log token pub-ip:2dd80147 being reversed back to the real IP 185.220.101.5 in a fraction of a second over a /24, with a throughput line extrapolating the full IPv4 space to about 61 minutes on one core.

Enrich First, Mask Second: An LLM-Safe VPC Flow Log Boundary

Say you run a security operations center and you want an AI copilot to help triage network traffic. The raw material is sitting right there: AWS VPC Flow Logs, a line per network connection, millions of them a day. Pasting them into a hosted large language model (an LLM, the kind of model behind Claude or ChatGPT) feels like it should just work. The problem is what a flow log line actually contains: your internal IP layout, your AWS account number, the identifiers of your network cards. Hand that to a third-party service and you have shipped a map of your private network to someone else’s computer, where it may be logged, cached, or used for training. ...

November 10, 2026 · 19 min · Scott Algatt
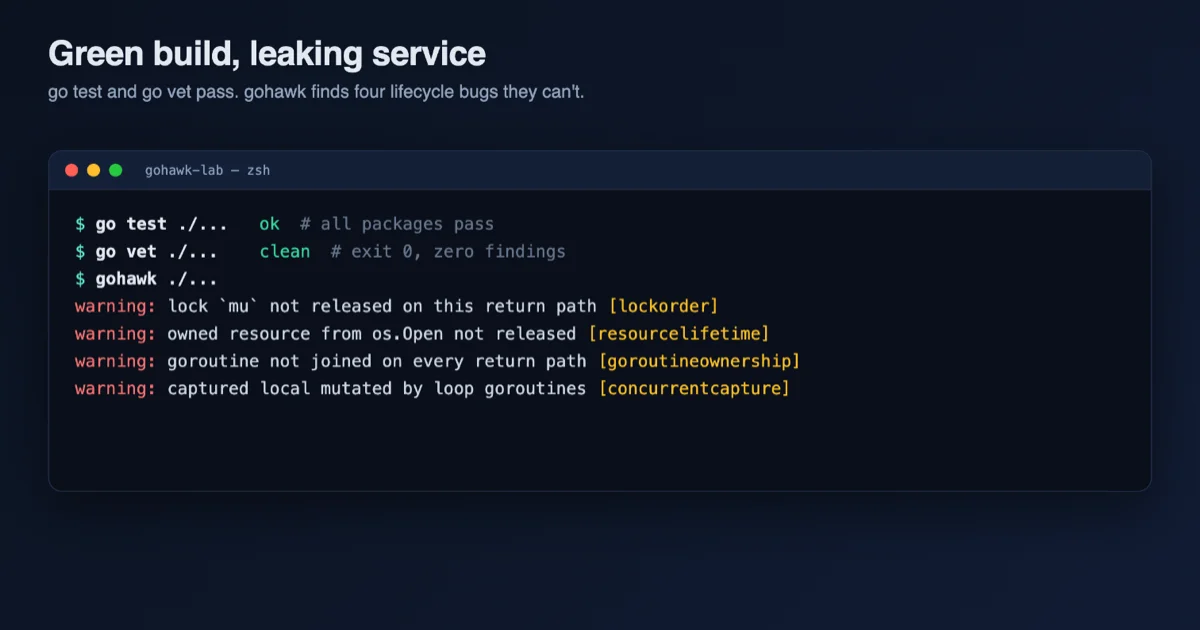
A terminal showing go test and go vet passing while gohawk reports four warnings: lockorder, resourcelifetime, goroutineownership, and concurrentcapture

Green Build, Leaking Service: Static Analysis for Go Concurrency and Resource Bugs with gohawk

A Go service can pass every test, clear go vet without a word, and still be quietly broken. The kind of bug I mean does not throw an exception or fail an assertion. It leaks. A file handle that never gets closed, a goroutine that nobody waits for, a lock that an early return skips over. Each one is invisible on a laptop with a single request in flight, and each one turns into a 3 a.m. incident once real traffic arrives: file descriptors exhausted, memory climbing with abandoned goroutines, a handler wedged on a lock that was never released. ...

November 6, 2026 · 21 min · Scott Algatt
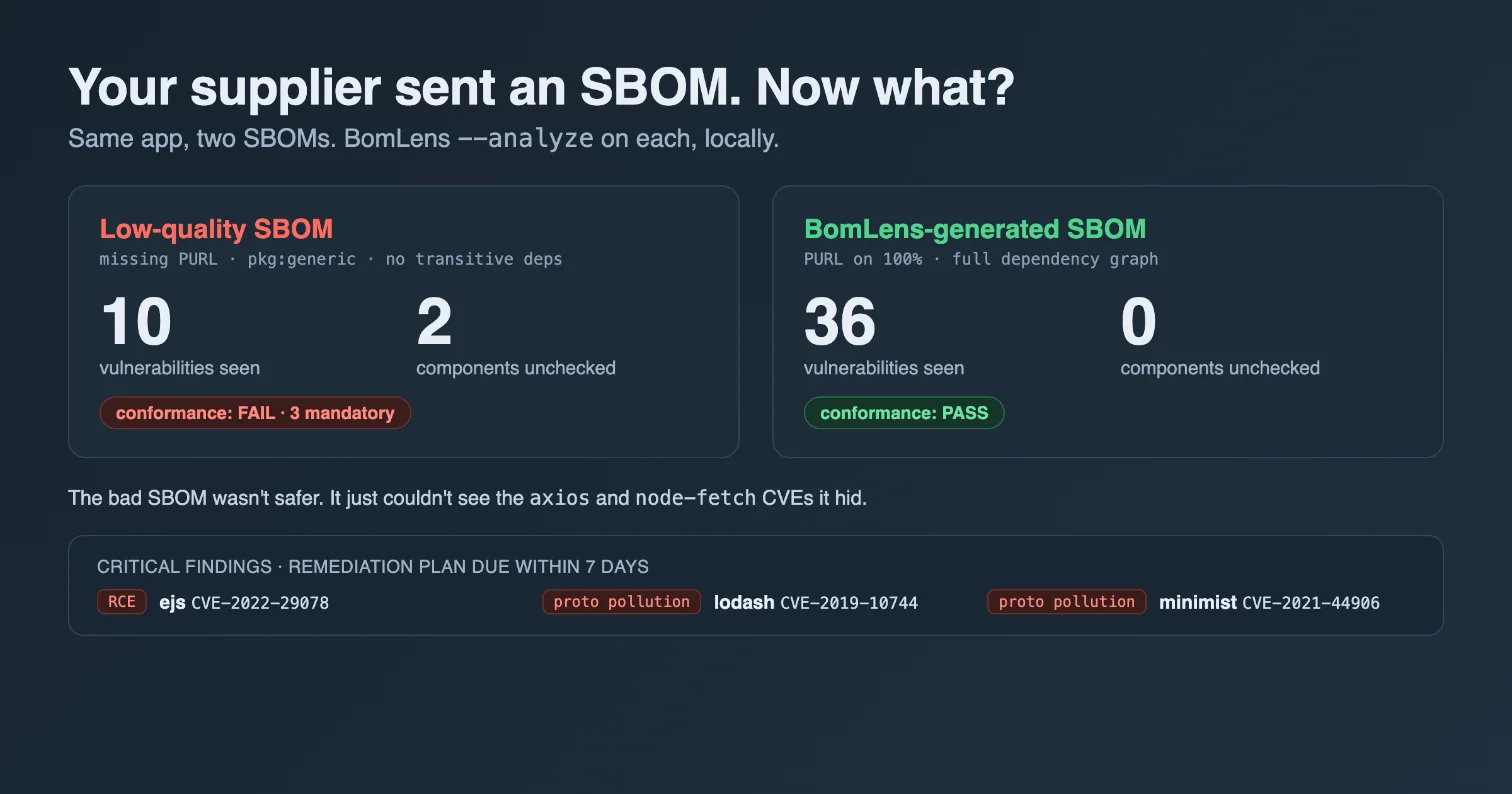
Two cards compared side by side. A low-quality SBOM shows 10 vulnerabilities seen, 2 components unchecked, and conformance FAIL with 3 mandatory failures. A BomLens-generated SBOM shows 36 vulnerabilities seen, 0 unchecked, conformance PASS. Below, three critical findings with a 7-day deadline: ejs CVE-2022-29078, lodash CVE-2019-10744, minimist CVE-2021-44906.

Your Supplier Sent an SBOM. Now What?: Turning CycloneDX Into Risk Decisions with BomLens

Here is a situation that has quietly become everyone’s problem. A vendor ships you a piece of software, and along with it a file called bom.json. It is a Software Bill of Materials, or SBOM: a machine-readable list of every open-source component inside that software, the same way a packaged food lists its ingredients. Regulators now ask for these, procurement teams now demand them, and your own security team now receives them. So the file lands in your inbox. Now what? ...

November 3, 2026 · 20 min · Scott Algatt
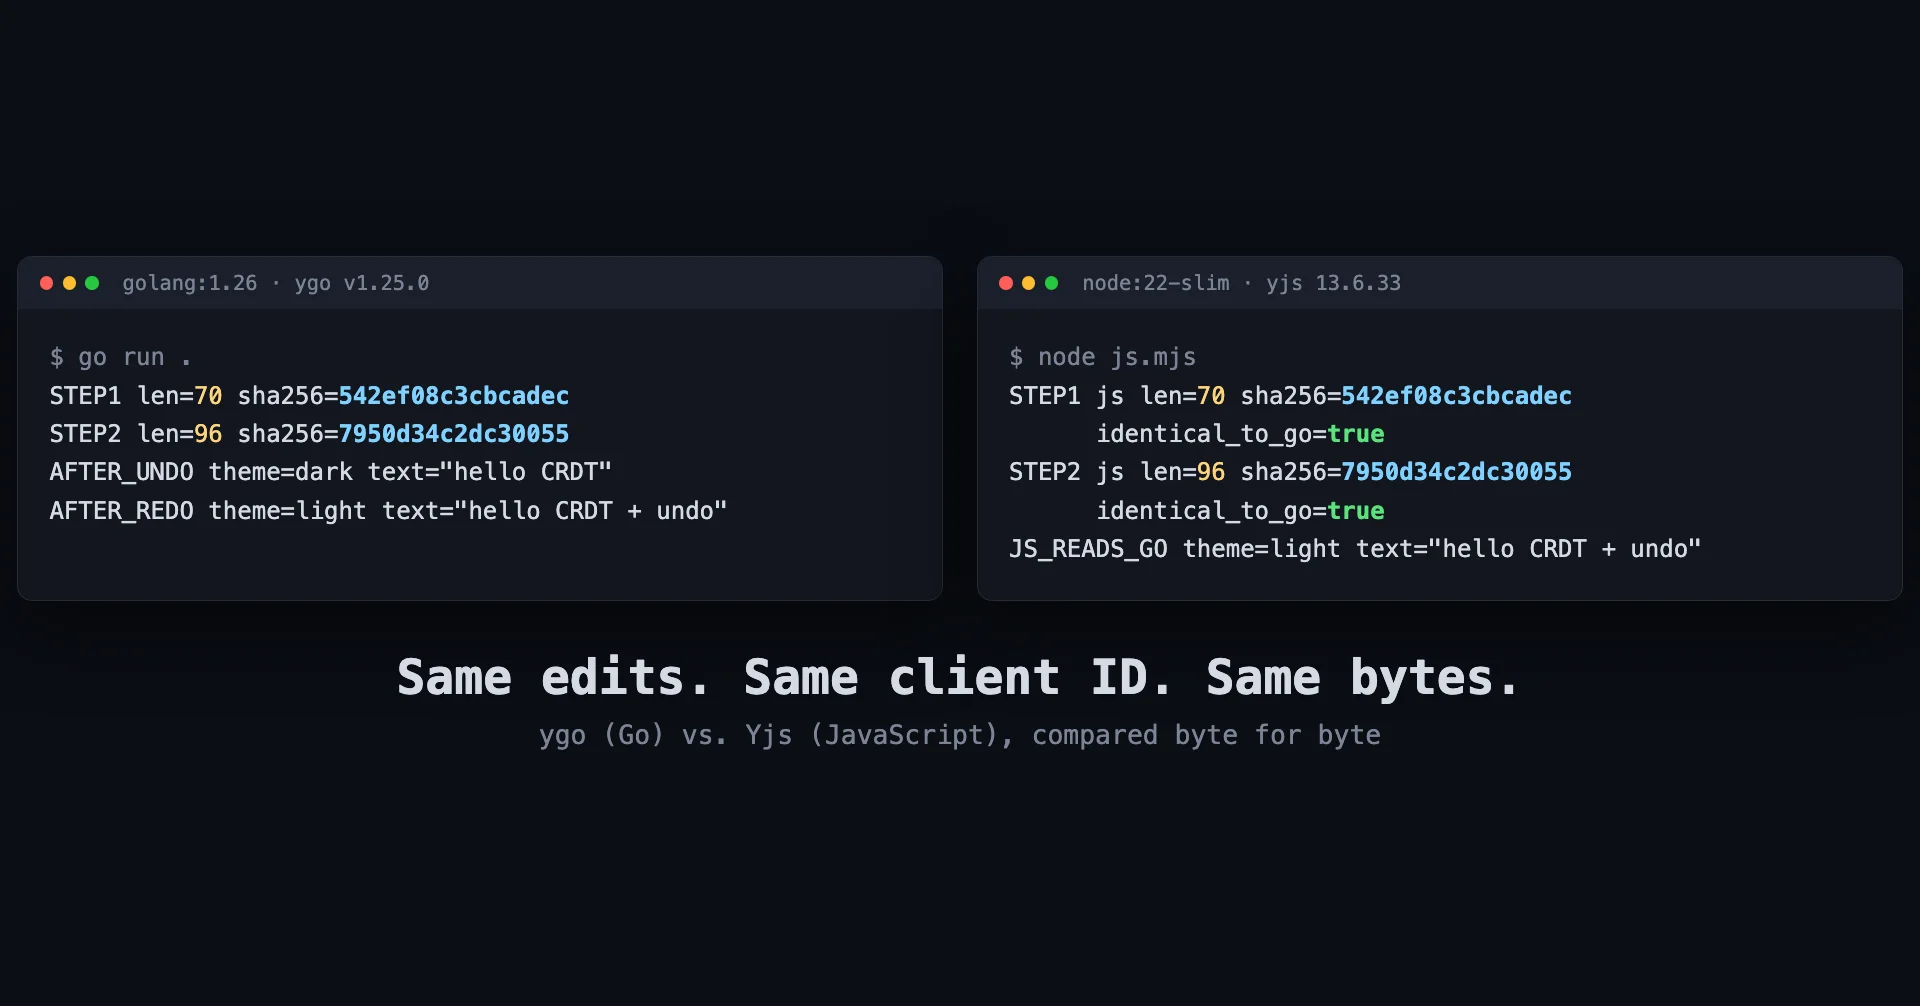
Two terminal panes side by side: a Go program using ygo prints a 96-byte update with sha256 7950d34c2dc30055, and a Node.js script using yjs 13.6.33 prints the same length and hash with identical_to_go=true

Same Bytes, Different Language: Testing ygo's Claim of Byte-for-Byte Yjs Compatibility

Every real-time collaborative editor has the same hard problem underneath it. Two people type into the same paragraph at the same moment, possibly while one of them is offline on a train, and when everything reconnects both screens have to end up showing exactly the same text without anyone’s edit vanishing. The family of data structures built to solve that is called a CRDT (Conflict-free Replicated Data Type): a structure designed so that copies of a document (called replicas) can accept edits independently and always merge to the same result, in any order, with no central referee deciding who wins. ...

October 16, 2026 · 19 min · Scott Algatt