Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
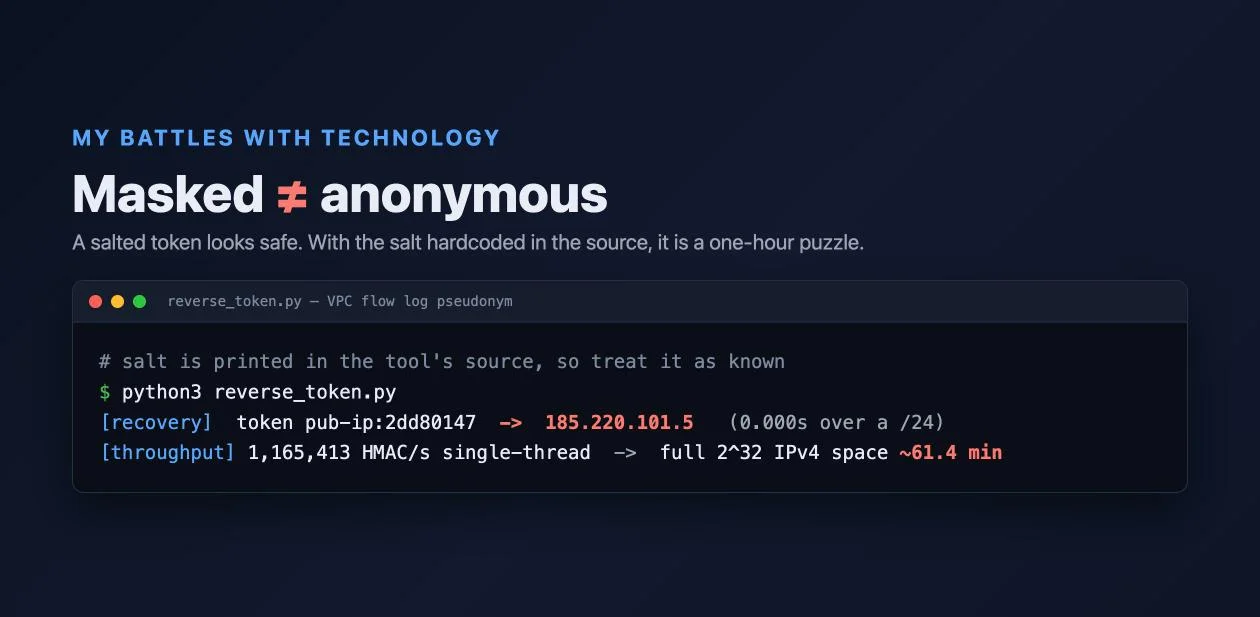
A terminal showing a masked VPC flow log token pub-ip:2dd80147 being reversed back to the real IP 185.220.101.5 in a fraction of a second over a /24, with a throughput line extrapolating the full IPv4 space to about 61 minutes on one core.

Enrich First, Mask Second: An LLM-Safe VPC Flow Log Boundary

Say you run a security operations center and you want an AI copilot to help triage network traffic. The raw material is sitting right there: AWS VPC Flow Logs, a line per network connection, millions of them a day. Pasting them into a hosted large language model (an LLM, the kind of model behind Claude or ChatGPT) feels like it should just work. The problem is what a flow log line actually contains: your internal IP layout, your AWS account number, the identifiers of your network cards. Hand that to a third-party service and you have shipped a map of your private network to someone else’s computer, where it may be logged, cached, or used for training. ...
November 10, 2026 · 19 min · Scott Algatt
Balance of AI ethics and security represented by scales of justice

Ethical Considerations in AI Security: Bias, Privacy, and Responsible Use

Note: This guide is based on research from AI ethics frameworks, academic publications on algorithmic fairness, NIST AI guidance, EU AI Act documentation, and industry best practices. The analysis presented draws from documented case studies and peer-reviewed research on AI ethics in security contexts. Readers should consult legal and compliance teams when implementing AI security systems to ensure alignment with applicable regulations and organizational values. AI-powered security tools promise faster threat detection, automated response, and reduced analyst workload. But these benefits come with ethical responsibilities that security teams must address proactively. Unlike traditional rule-based systems, AI models can exhibit bias, make opaque decisions, and create privacy risks that traditional security tools don’t. ...

December 6, 2025 · 18 min · Scott

Decentralizing AI: A Guide to Building Scalable and Secure Decentralized AI Platforms

Decentralizing AI: A Guide to Building Scalable and Secure Decentralized AI Platforms Note: This guide is based on research from decentralized AI projects (Ocean Protocol, Fetch.ai, SingularityNET), federated learning frameworks (Flower, PySyft), and academic papers on privacy-preserving machine learning. Code examples are derived from official documentation and community implementations. Decentralized AI addresses fundamental challenges in traditional centralized AI systems: data privacy, model ownership, computational bottlenecks, and single points of failure. According to research from the IEEE and ACM, decentralized AI encompasses three primary approaches: federated learning (training on distributed data without centralization), blockchain-based model registries (transparent model provenance), and distributed inference (computational load distribution). ...

March 28, 2025 · 10 min · Scott