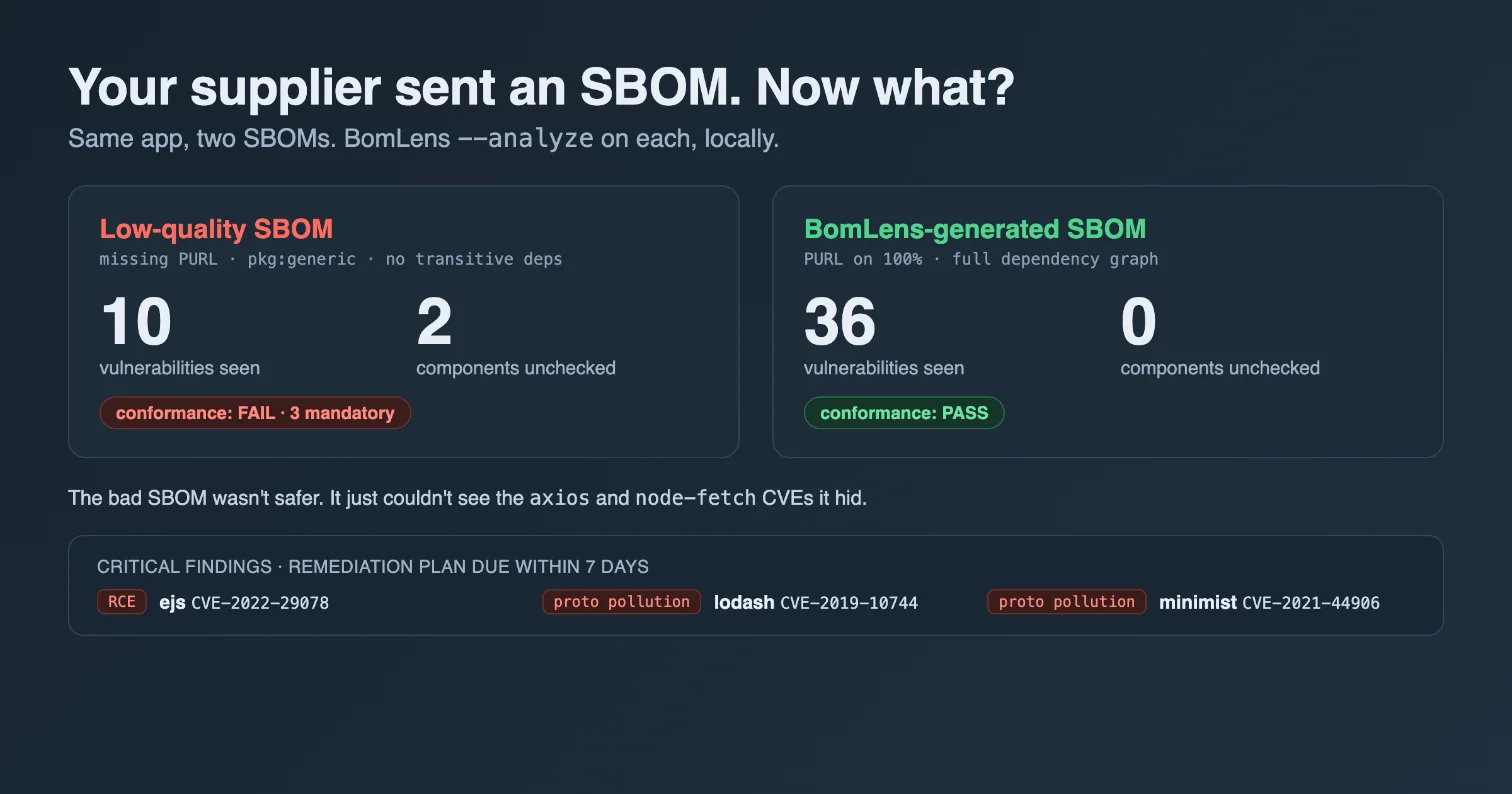
Your Supplier Sent an SBOM. Now What?: Turning CycloneDX Into Risk Decisions with BomLens
Here is a situation that has quietly become everyone’s problem. A vendor ships you a piece of software, and along with it a file called bom.json. It is a Software Bill of Materials, or SBOM: a machine-readable list of every open-source component inside that software, the same way a packaged food lists its ingredients. Regulators now ask for these, procurement teams now demand them, and your own security team now receives them. So the file lands in your inbox. Now what? ...