Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
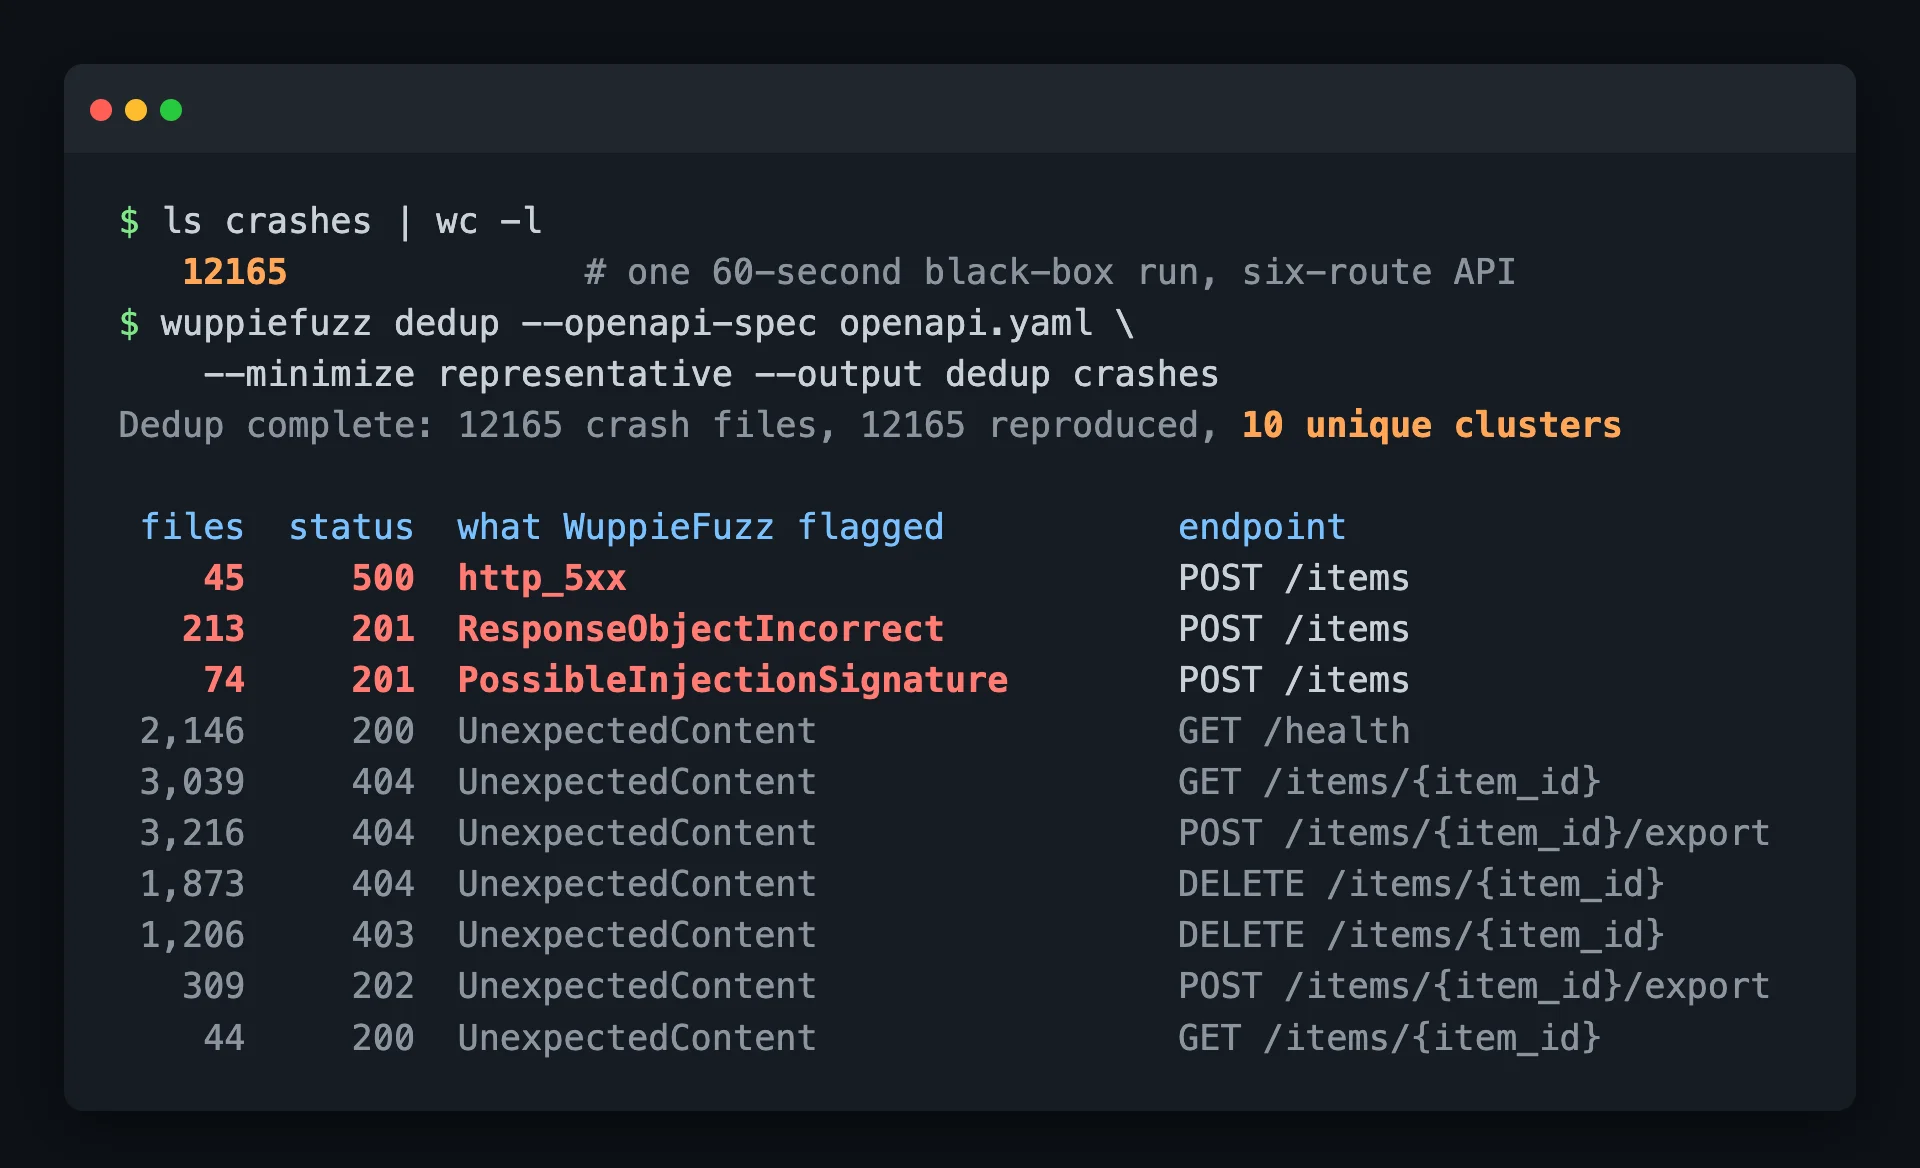
A terminal showing ls crashes | wc -l returning 12165, then wuppiefuzz dedup reducing them to 10 unique clusters. Three clusters are highlighted in red: a 500 on POST /items, an incorrect response object, and a possible injection signature. The other seven are UnexpectedContent on every endpoint.

12,165 Crashes in 60 Seconds: Fuzzing a REST API with WuppieFuzz

Most REST APIs ship with two kinds of tests: unit tests that check functions in isolation, and integration tests that walk the happy path. “Create an item, read it back, delete it, get a 204.” Those tests are written by the same people who wrote the code, so they test the inputs those people expected. Nobody writes the test that sends a 65-character name, a quantity of 2^64, or a DELETE for an item that was never created, because nobody thought of it. ...

October 23, 2026 · 33 min · Scott Algatt
A visual representation of an intercepting proxy sitting between a client and a server, with traffic flows being inspected in a terminal-like view.

Intercepting Opaque Traffic: A mitmproxy Security Regression Harness

Most security monitoring tools rely on server-side logs or cloud-native telemetry. But what happens when the client is opaque? When a mobile app, a single-page application (SPA), or a proprietary service is behaving in ways the server doesn’t fully document, you need a way to look at the wire directly. This post also marks the beginning of a new experiment: The Rabbit Hole Series. Every Friday, a “Rabbit Hole Generator” I built (which I later took apart in its own post) spits out a new technical topic for me to explore for 30 minutes. This week, the generator gave me mitmproxy. ...

April 3, 2026 · 5 min · Scott Algatt