Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
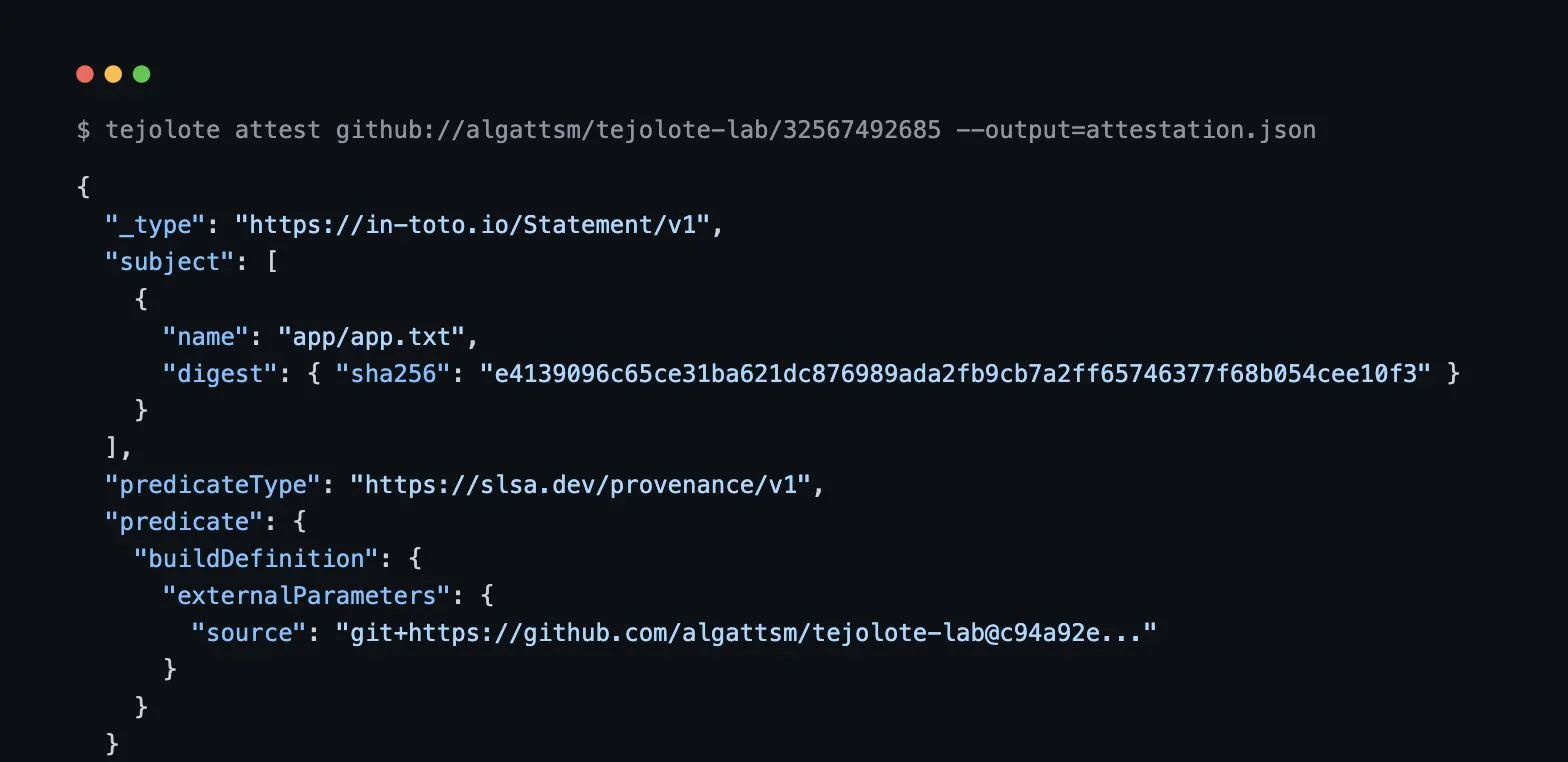
Terminal output showing a real SLSA provenance JSON statement generated by Tejolote from a live GitHub Actions run, with a matching sha256 artifact digest

Provenance From the Outside: Attesting Real Builds with Tejolote

A signature on a piece of software proves someone with a key signed it. It doesn’t prove much about where that software actually came from: what source it was built from, what process built it, or whether anything happened to it between “code written” and “artifact shipped.” Provenance is the term for closing that gap: a verifiable record tying a specific commit, through a specific build process, to a specific output, in a way that’s checkable rather than just asserted. ...

August 28, 2026 · 13 min · Scott Algatt

Supply Chain Cyberattacks: Lessons from the UNFI Breach

Supply Chain Cyberattacks: Lessons from the UNFI Breach The June 2025 cyberattack on United Natural Foods Inc. (UNFI) exposed critical vulnerabilities in food distribution infrastructure, disrupting shipments to over 30,000 stores including Whole Foods. This technical deep dive analyzes the attack’s mechanisms, operational impacts, and actionable security controls for supply chain resilience. Incident Timeline and Impact Analysis Attack Chronology June 5, 2025: Initial breach detected via anomalous EDI traffic patterns June 6: UNFI takes critical systems offline, including: Transportation Management System (TMS) Warehouse Management System (WMS) Electronic Data Interchange (EDI) platforms June 9: SEC filing discloses “material operational disruption” June 11: Partial restoration of cold chain logistics systems [Diagram: UNFI System Architecture and Compromise Points] ...

November 2, 2023 · 4 min · Scott Algatt