Your OCSF Pipeline Is Lying to You: Catching Silent Data Loss with ocsfkit
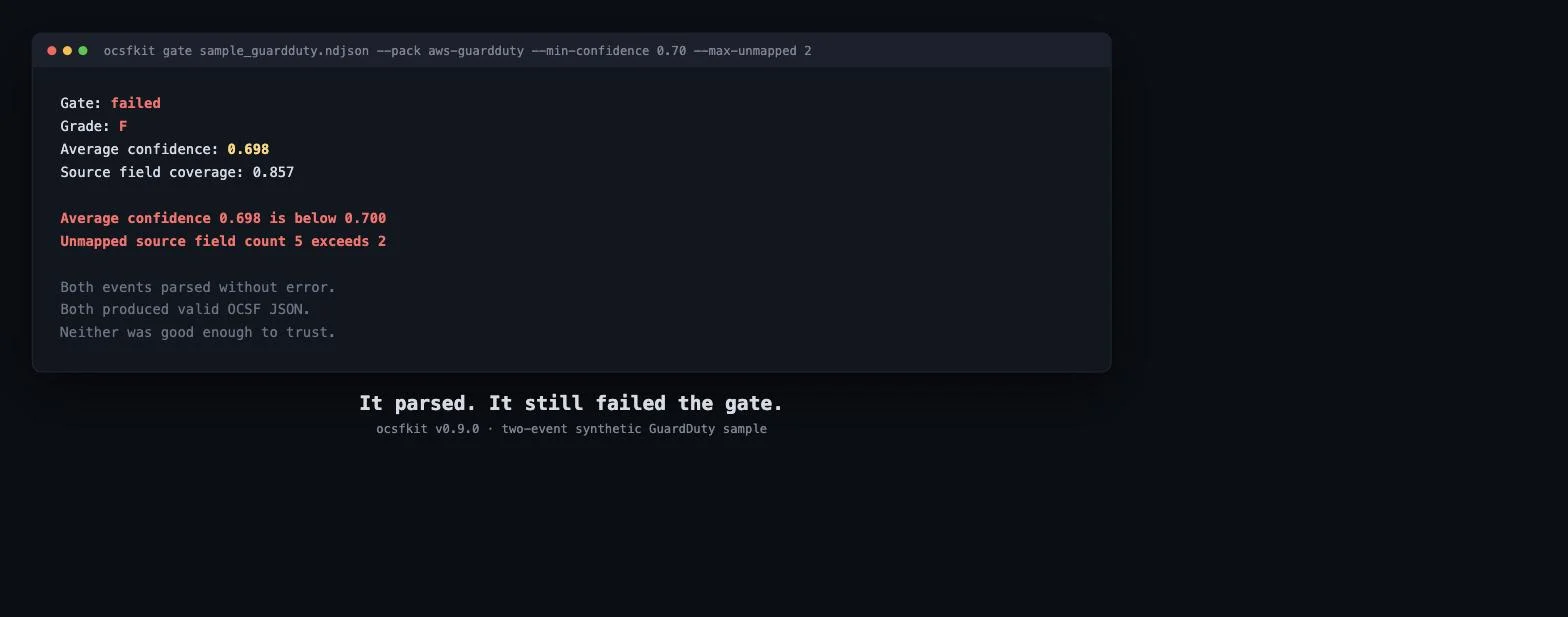
This week’s Rabbit Hole Generator pick was ocsfkit, and it’s aimed at a failure mode that doesn’t look like a failure at all: a security event that parses successfully, lands in your SIEM (Security Information and Event Management platform, the system that ingests and correlates security logs), and gets treated as trustworthy, while a real chunk of what it originally meant never made it through the translation. That translation step is normalization: taking a vendor’s raw event format (AWS GuardDuty’s JSON, Okta’s login logs, whatever a tool emits) and reshaping it into a common schema so different security tools can actually talk about the same event the same way. OCSF (Open Cybersecurity Schema Framework) is the industry’s current attempt at that common schema. The part nobody’s tooling handles well is what happens to the fields that don’t map cleanly. Most pipelines either silently drop them or silently guess, and a downstream analyst has no way to tell the difference between a field that was confidently mapped and one that was quietly invented. ...