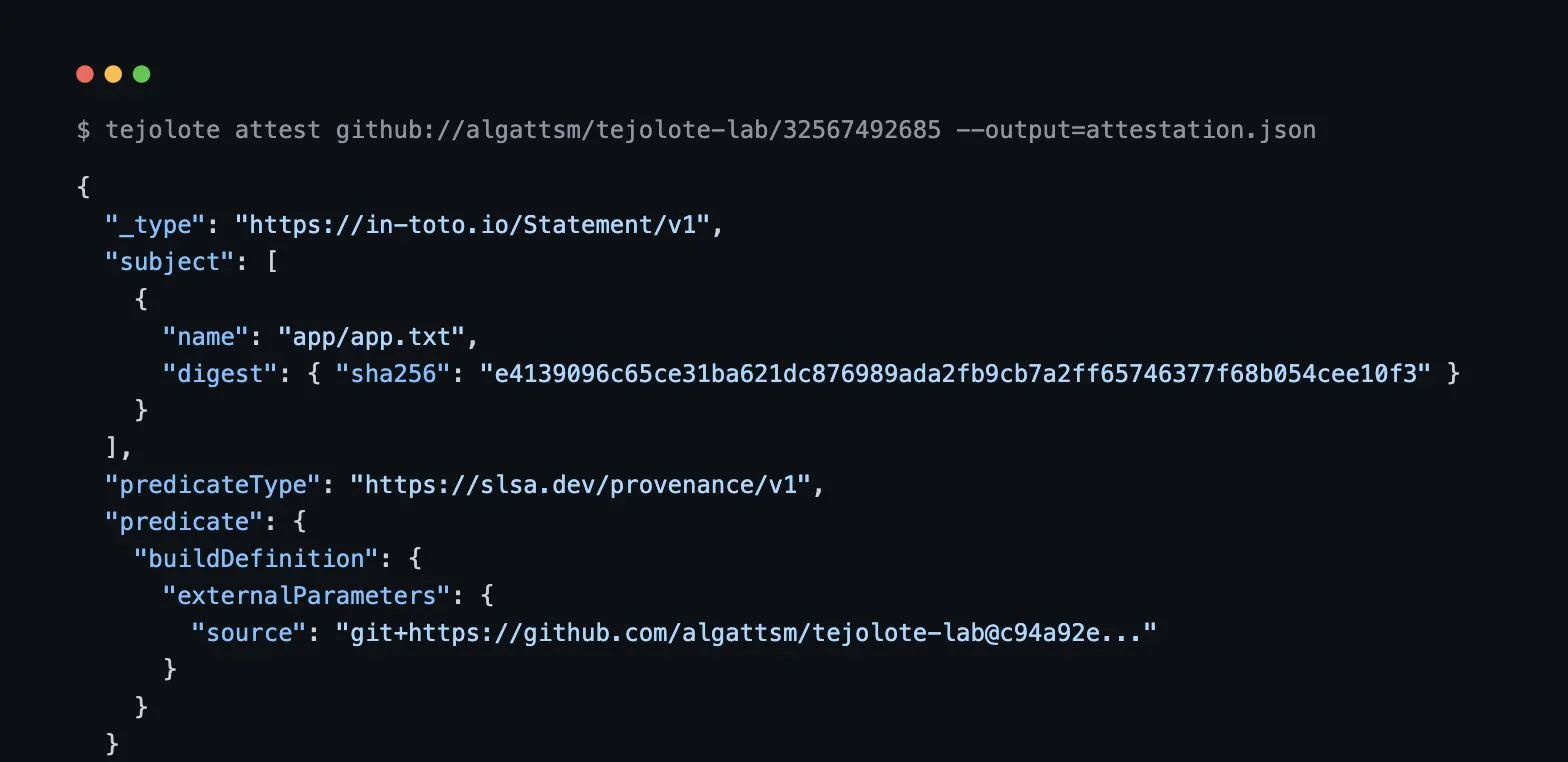
Provenance From the Outside: Attesting Real Builds with Tejolote
A signature on a piece of software proves someone with a key signed it. It doesn’t prove much about where that software actually came from: what source it was built from, what process built it, or whether anything happened to it between “code written” and “artifact shipped.” Provenance is the term for closing that gap: a verifiable record tying a specific commit, through a specific build process, to a specific output, in a way that’s checkable rather than just asserted. ...