Beyond CVEs: Verifying Supply Chain Provenance with Macaron
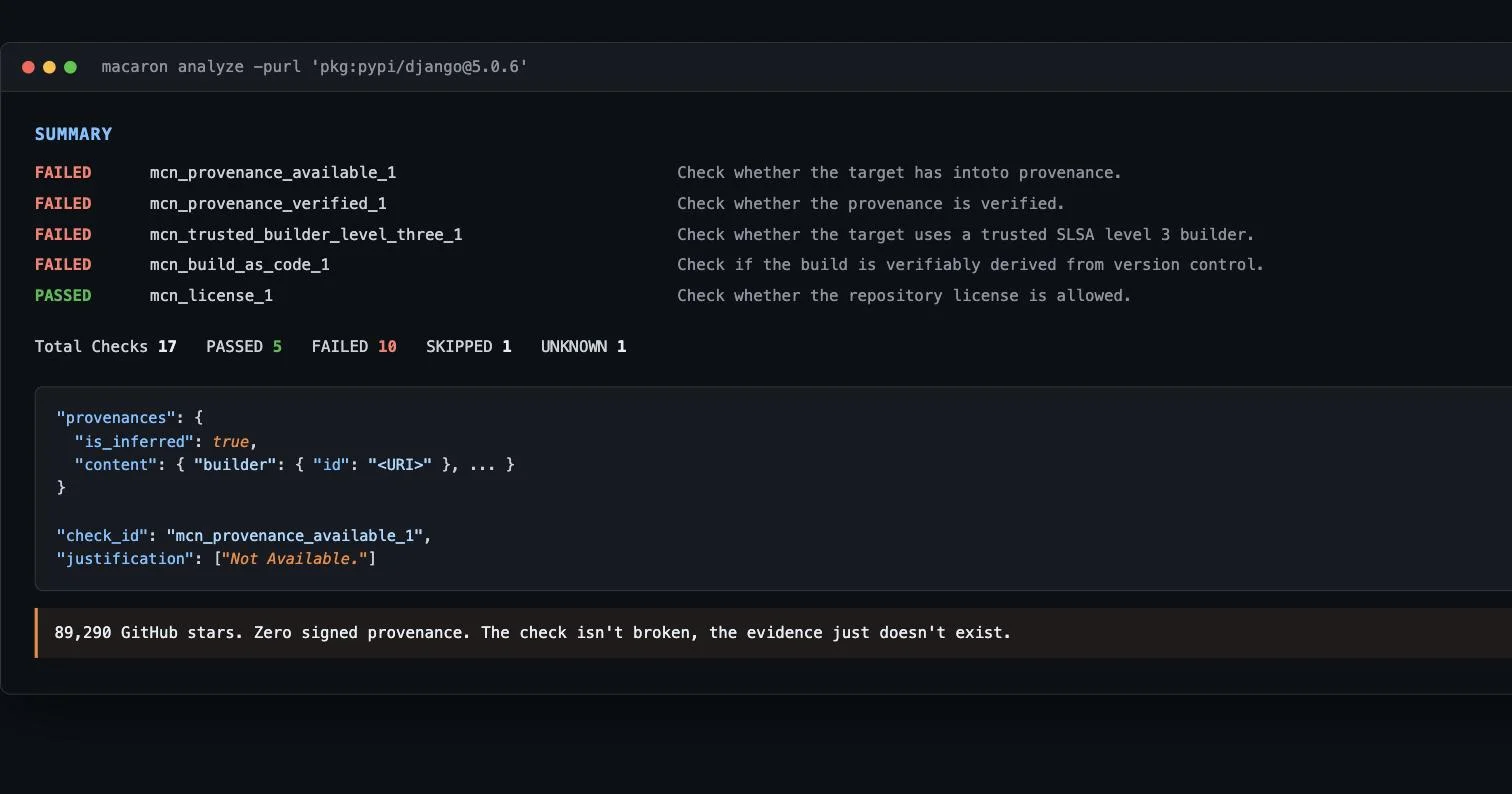
The Rabbit Hole Generator gave me Macaron this week, Oracle’s open-source tool for checking software supply chain security. My first instinct was to file it next to every other dependency scanner I’ve used: point it at a package, get a list of CVEs back. That’s not what it does, and the gap between those two things turned out to be the actual point. A vulnerability scanner answers “does this package version have a known CVE.” Macaron answers a different question: “was this artifact actually built from the source code we think it was, by a process we can verify, with evidence that isn’t just the vendor’s word for it.” Those sound similar. They aren’t. A package can have zero known CVEs and still have no evidence at all connecting the file you pip installed to the GitHub repo everyone assumes it came from. ...