Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
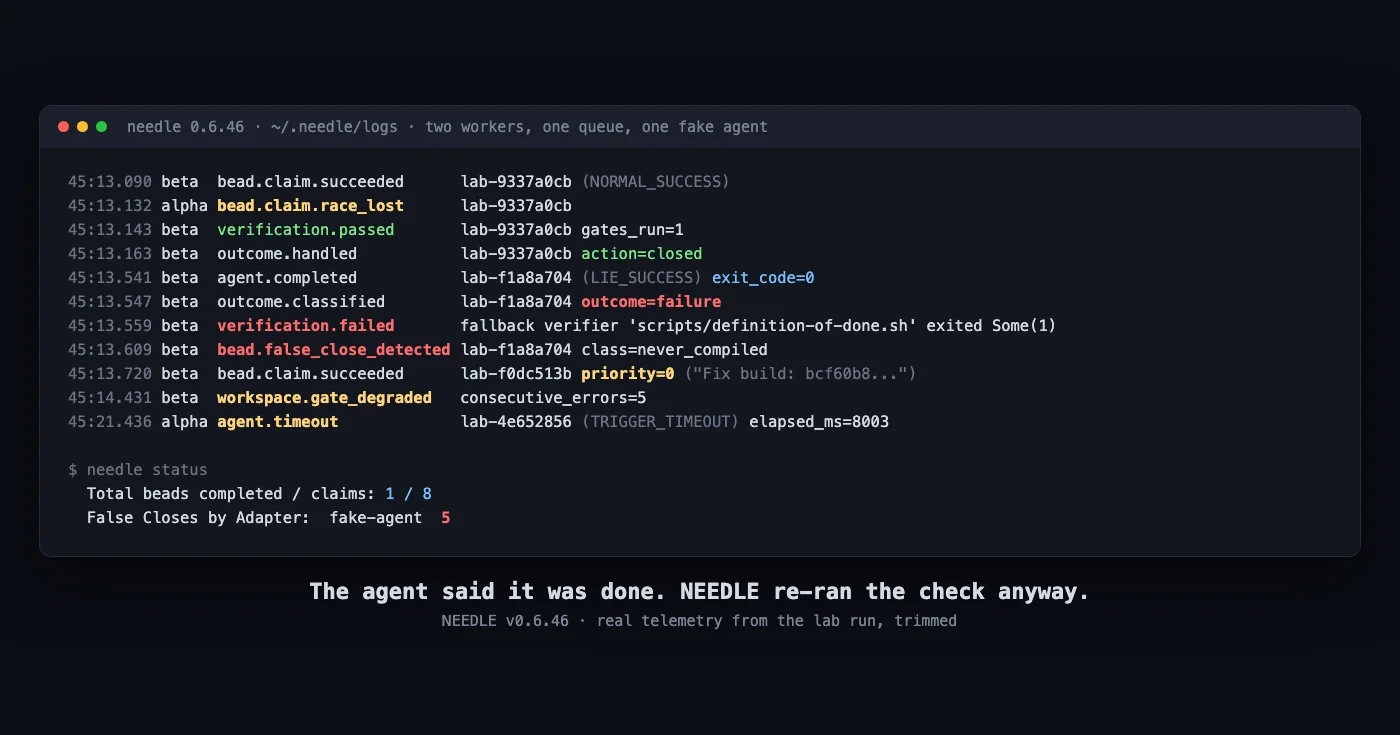
Terminal output from a NEEDLE lab run: a fake agent exits 0 on a bead it lied about, NEEDLE re-runs the definition of done, the verification fails, a false close is detected, and a priority-0 Fix build bead is filed automatically

Boring on Purpose: Wrapping Coding Agents in NEEDLE's State Machine

The Rabbit Hole Generator gave me NEEDLE this week, and it lands right on a question I keep running into: once you let a coding agent run unattended, who decides whether it actually did the job? Most of the excitement around coding agents is about making them smarter. NEEDLE is interested in something much less glamorous. It assumes the agent is unpredictable, wraps it in a loop where every step around the agent is fixed and logged, and then refuses to take the agent’s word that it finished. I didn’t want to point a real AI model with its permission prompts switched off at anything, so I ran the whole thing against a fake agent: a 20-line shell script that succeeds, fails, hangs, and lies on cue. The lying one turned out to be the most interesting part. ...
October 9, 2026 · 35 min · Scott Algatt
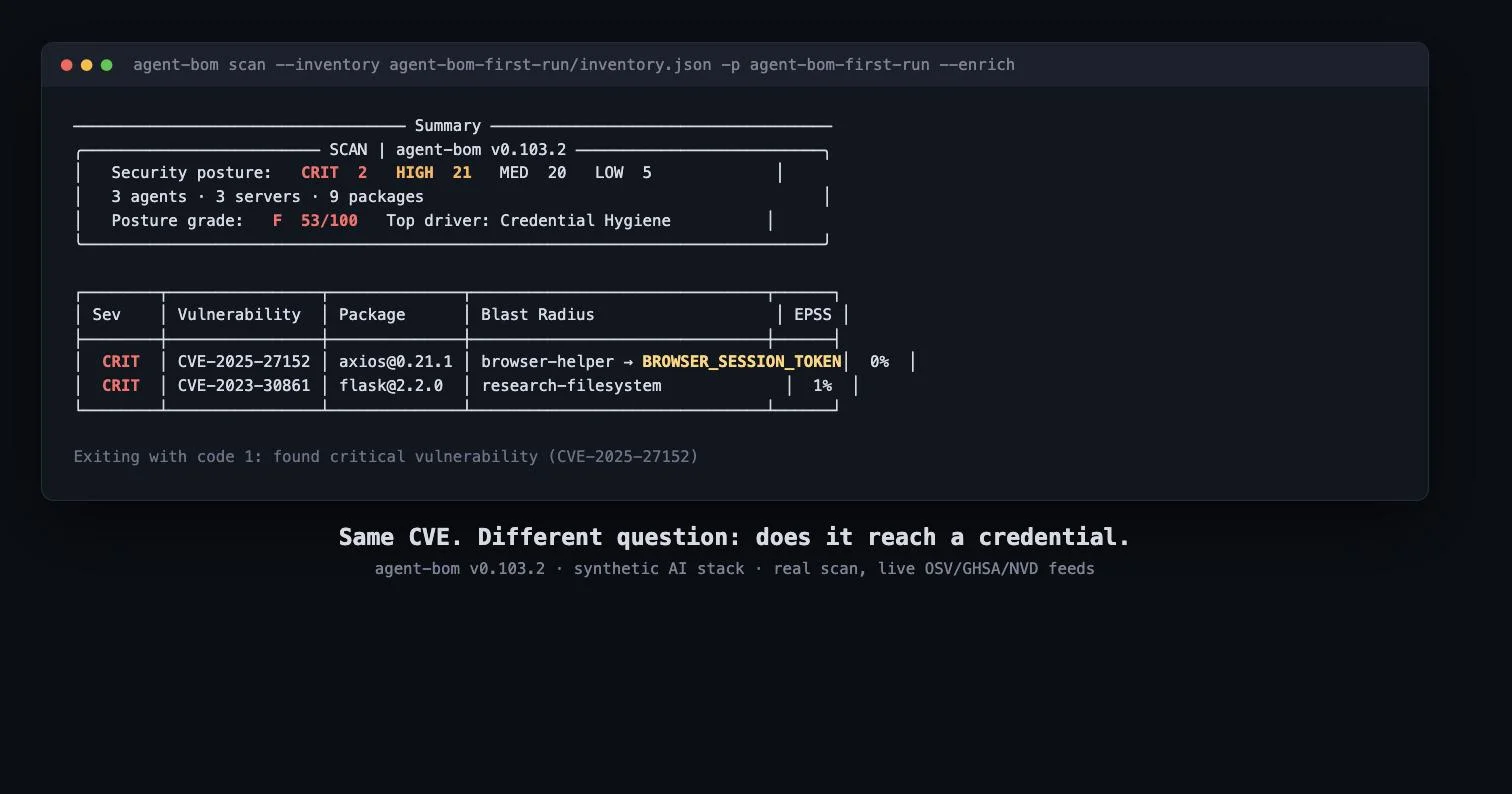
Terminal output from agent-bom scan showing a security posture summary with 2 critical, 21 high, 20 medium, and 5 low findings, a posture grade of F, and a findings table naming a CVE in axios with a blast radius chain ending in a browser session token

The CVE List Isn't the Point: Mapping Blast Radius in AI Infrastructure with agent-bom

The Rabbit Hole Generator gave me agent-bom this week, and it landed on a question I’ve been circling for a while: what does a vulnerability scanner actually owe you once “AI agent” and “MCP server” show up in your stack next to the usual packages and containers? A traditional scanner tells you a package has a CVE. It stops there. It doesn’t know that package sits inside an MCP server (a small local process that gives an AI agent tools like “read this file” or “run this shell command”), and it definitely doesn’t know that server has an AWS_SECRET_ACCESS_KEY sitting in its environment. agent-bom is built specifically to answer the next question a CVE list never does: from this vulnerable package, what can actually be reached? ...

September 18, 2026 · 12 min · Scott Algatt
A digital rabbit made of glitching code and binary dissolves into a Matrix-style tunnel of green cascading numbers, descending toward a glowing terminal at the bottom of the rabbit hole

Zero Learning Mode: Building the Rabbit Hole Generator

Every post in this series starts the same way: I open Notion on a Friday and there’s a tool waiting for me that I didn’t pick. That’s on purpose, and it took me building an actual automation to get there. For a long time before this series existed, I was stuck in what I’d call zero learning mode. I like learning new things, genuinely, but I’d sit down with time set aside and just… not know what to point it at. Too many options, no filter, no momentum. I wasn’t short on curiosity, I was short on a starting point. So I built one: an n8n workflow that picks a tool for me every week, does the research, and hands me a scoped 30-minute exercise, no decision required on my end except whether to actually do it. ...

September 4, 2026 · 8 min · Scott Algatt