Feeling overwhelmed by AI? Learn the Centaur Mindset. Read More →
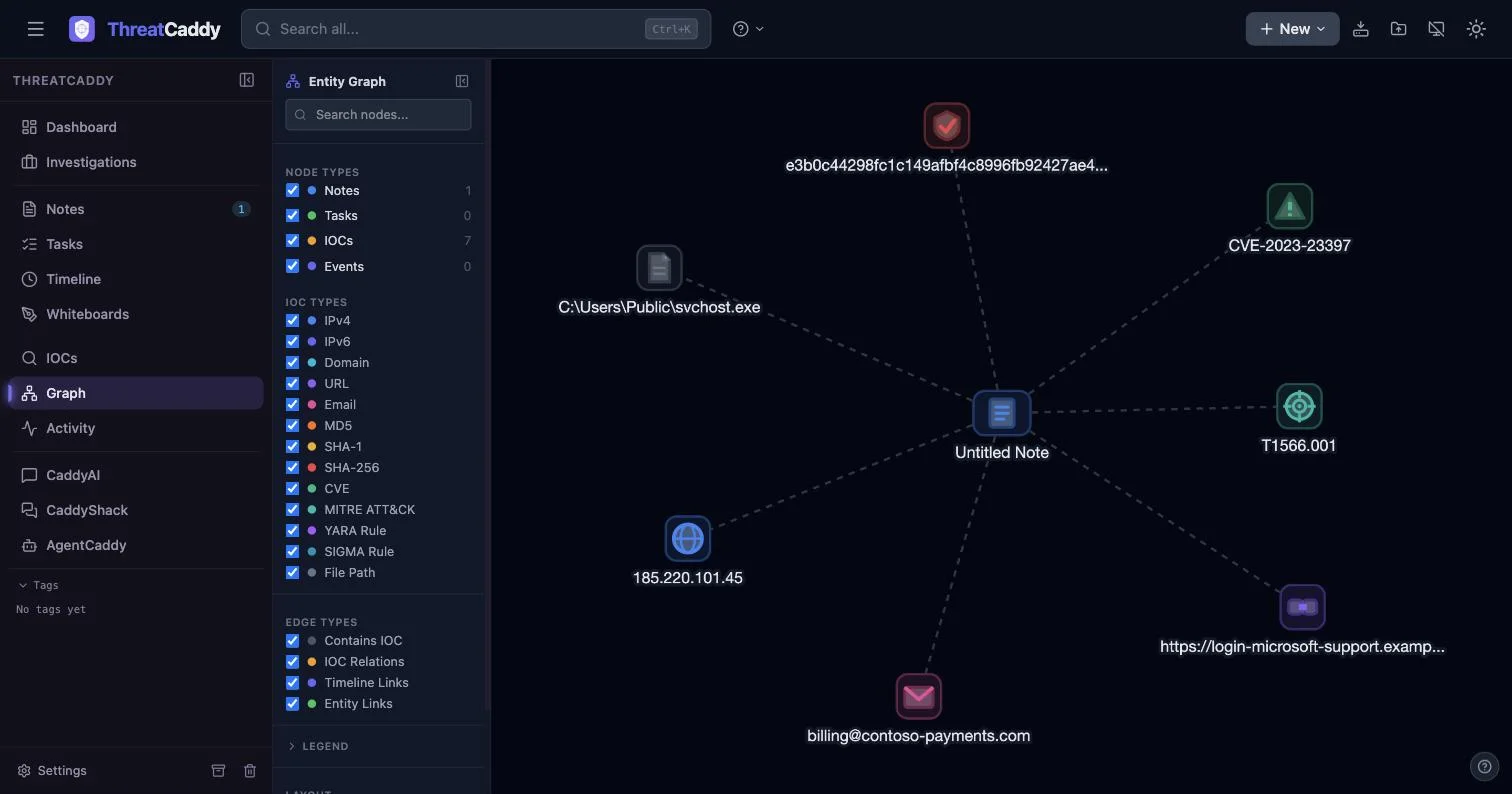
A ThreatCaddy entity graph showing a note connected to seven auto-extracted IOCs: an email, URL, IPv4, SHA-256, CVE, ATT&CK ID, and file path

The Browser Is the Case File: A Local-First Investigation Workspace with ThreatCaddy

Most incident response tooling forces a bad choice on you early in a case. Either you’re in a spreadsheet or a plain notebook with no structure, or you’re setting up a cloud platform with procurement friction, a rigid schema, and a data residency conversation before you’ve even confirmed the phishing email is real. Neither one matches the actual shape of early-stage IR work: messy notes, indicators that need pulling out and tracking, and relationships between them that you don’t know yet. ...

August 21, 2026 · 9 min · Scott Algatt
A complex workflow diagram in the Dify UI showing LLM nodes and tool connections.

Beyond the Prompt: Orchestrating LLM Apps with Dify

Most “agent frameworks” are libraries that push the hard parts of production (orchestration, secrets, versioning, and audit logging) into ad-hoc glue code. As teams move from “chatting with a PDF” to shipping internal copilots, the need for a governed, observable runtime becomes undeniable. This is where Dify enters the stack. It’s a self-hostable “LLM app runtime” designed to turn agentic prototypes into real business services. What is Dify used for in LLM application development? Dify is an open-source LLM application development platform that provides a unified workflow engine, model gateway, and RAG subsystem. It allows developers to model AI applications as explicit directed acyclic graphs (DAGs), enabling governed orchestration of LLM calls, external tools, and retrieval policies with built-in operational telemetry and multi-tenant isolation. ...

May 29, 2026 · 4 min · Scott Algatt

Access Your Kubernetes Cluster from Any Device on Your WiFi -- No VPN Client Required

The Goal I have a DigitalOcean Kubernetes cluster running services like n8n (workflow automation), SearXNG (search), PostgreSQL, and Redis. I also have a Raspberry Pi 5 running OpenWrt as my home router. I wanted every device on my WiFi – laptops, phones, tablets – to be able to access my K8s services directly by ClusterIP, without installing Tailscale (or any VPN client) on each device. The result: my wife can open http://10.245.15.122:5678 on her laptop and hit n8n. My iPad can reach SearXNG. Any device on the WiFi just… works. The OpenWrt router handles the encrypted tunnel transparently. ...

May 22, 2026 · 8 min · Scott

The Final Architecture: From $198/Month to $74/Month with Claude Code

Series: How I Used Claude Code to Slash My Cloud Bill by 63% Part 1: The $198/Month Wake-Up Call Part 2: Migrating 7 Static Sites to Cloudflare Pages Part 3: Killing the Load Balancer with Cloudflare Tunnel Part 4: Building a Home Router with a Raspberry Pi 5 Part 5: Connecting Everything with Tailscale Part 6: The Final Architecture - $74/mo and Zero Regrets (you are here) The Before Architecture Here’s what I was running before this project started: ...

May 15, 2026 · 11 min · Scott

Connecting Everything with Tailscale: K8s Meets Home Network

Series: How I Used Claude Code to Slash My Cloud Bill by 63% Part 1: The $198/Month Wake-Up Call Part 2: Migrating 7 Static Sites to Cloudflare Pages Part 3: Killing the Load Balancer with Cloudflare Tunnel Part 4: Building a Home Router with a Raspberry Pi 5 Part 5: Connecting Everything with Tailscale (you are here) Part 6: The Final Architecture - $74/mo and Zero Regrets The Problem: Private Access Without Public Exposure After the Cloudflare Tunnel work in Part 3, I had one service (n8n) accessible through a tunnel and everything else locked down inside the Kubernetes cluster. But I had other internal services I wanted to reach from my home network – things like SearXNG, Redis Commander, and the Kubernetes dashboard. None of these should be publicly accessible. I don’t want a public endpoint for my search engine or my database admin tool. ...

May 8, 2026 · 9 min · Scott